Feuerfest

Just the private blog of a Linux sysadmin

Blogroll & Links

Back in the days we used to have a large list of links to other blogs we like in the sidebar. This is the same, just on a separate page.

Blogs

UberBlogr Webring.

Also my blog is part of the UberBlogr Webring (FAQ in german). Via the links below you can go back & forth or visit the UberBlogr site to read what this is all about. The "Random blog" link will take you to a random blog from all members participating in the Webring.

«Previous | UberBlogr Webring (Random blog) | Next»

Links

TheRegister.com: Technology news website.

Golem.de: German technology news website. Sadly their quality constantly deteriorates and is nowhere as in the 2000s. (Several ownership changes between 2006 - 2013. In 2013 the original founders left. Since then content quality is getting more & more shallow..)

Heise.de: German technology news website. Legendary through the early 2000s also for the accompanying C't magazine. Like Golem also on a steady decline as their better journalists all left or are enjoying their retirement.

Übermedien.de: German magazine for media critique.

Funny sites

Infosec Reactions and DevOps Reactions and DBA Reactions: Are long dead Tumblr blogs, but I still enjoy going through their archive from time to time.

thedailywtf.com: Funny IT stories, they call themselves "your how-not-to guide for developing software".
Comments

gethomepage 1.0 release and new security parameter introduced

gethomepage.dev: https://gethomepage.dev/assets/homepage_demo_clip.webp

homepage (GitHub) - the dashboard I use to keep an overview of all the services I run in my LAN released their 1.0 version yesterday on March 14th 2025.

With that they introduced a new parameter to limit which hosts can show the dashboard. I haven't yet read about why this was introduced, but it's fixed quickly.

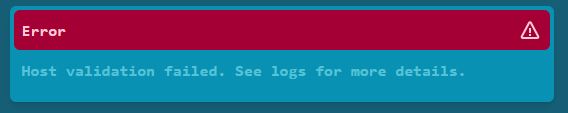
As Watchtower does all the maintenance work for the containers running on my installation of Portainer I was already greeted with the following error message:

In the logfile for the container running homepage I saw the following error:

[2025-03-15T16:54:13.497Z] error: Host validation failed for: portainer.lan:3000. Hint: Set the HOMEPAGE_ALLOWED_HOSTS environment variable to allow requests from this host / port.

As I don't use a separate IP or hostname for the dashboard and just forward the port 3000/tcp towards the homepage-container I access it using the hostname of my Portainer host. Therefore this message makes sense.

Luckily the documentation for the newly required environment variable is already on their homepage: https://gethomepage.dev/installation/#homepage_allowed_hosts

Armed with this knowledge we can change the stack file (Portainers term for a docker-compose file - not to be confused with the docker swarm command docker stack) and introduce the HOMEPAGE_ALLOWED_HOSTS parameter. I added the IP-address too, in case the DNS servers in my LAN should stop working.

services:
  homepage:
    image: ghcr.io/gethomepage/homepage:latest
    container_name: homepage
    ports:
      - 3000:3000
    environment:
      HOMEPAGE_ALLOWED_HOSTS: 192.168.178.21:3000,portainer.lan:3000
    volumes:
      - /opt/docker/homepage.dev/config:/app/config # Make sure your local config directory exists
      - /var/run/docker.sock:/var/run/docker.sock # (optional) For docker integrations
      - /opt/docker/homepage.dev/icons:/app/public/icons # icons, reference as /icons/picture.png in YAML

After that just hit the "Update the stack" button and it's working again.

Comments

One big step for Mastodon to rule the social media world

Photo by Jonathan Cooper: https://www.pexels.com/photo/animals-head-on-exhibition-9660890/

For years Mastodon had one prominent missing feature. You wouldn't see all replies to a toot (that's the term for "Tweet" in the Mastodon world) because of the federated nature of Mastodon. There were exceptions, but in general it means that you have to open the post on the Mastodon instance it originated from. Only then you would be able to read all comments.

Naturally this feature was sought after for years. One GitHub issue was opened in 2018 (Mastodon #9409: Fetch whole conversation threads).

Now it seems the biggest technical part has been resolved! In Mastodon #32615: Add Fetch All Replies Part 1: Backend user sneaker-the-rat did all the basic work to incorporate that functionality into the backend of Mastodon. And while he mentions that there is still work to do the Mastodon community so far seems happy that this issue is finally getting fixed providing a much smoother experience for everyone.

Comments

Every recommendation algorithm, ever

Photo by Tima Miroshnichenko: https://www.pexels.com/photo/a-computer-monitor-5380589/

Algorithm: Yo, look here! On the start page! A recommendation for a movie/video/song/article from a genre you've never watched/listened to/read! But it's one of our own productions!

Algorithm: Or content you've already consumed 4 weeks ago. You surely like to re-consume it again while that memory is still fresh, right?

Algorithm: On the other hand we have content you rated with a "Like" years ago. - But we completely ignore your recent interests and likes when proposing those.

Me: Uh, where is the notice about this new piece of content, which was released today, from the series I'm watching since months and always consume each new part directly on the day of its release? Do I really have to use the search?

Algorithm: Uh.. Can I interest you in some World War documentation?

*sigh* Every. Single. Time.

Folks! Don't declare your algorithm helps users finding new interesting content, when all it does is advertising.

Comments

uMatrix: Fehler 403 bei Aufruf von Links im web.de/GMX Webmailer beheben

Dall-E

Das Problem

Bekannte erhalten an ihre GMX-Mailadresse eine Mail. Diese enthält klickbare Links. Bei einem Klick landet man jedoch nicht auf der GMX-Weiterleitungsseite und anschließend auf der Seite auf die man eigentlich aufrufen möchte.
Stattdessen bekommt man die Fehlermeldung:

Ups, hier hat sich ein Fehler eingeschlichen...
Fehler-Code: 403

Bei einer web.de Adresse ist es genau so. Gut, das ist zu erwarten, da sowohl GMX als auch web.de zur gleichen Firma gehören und die Webmailer die gleichen sind. Lediglich etwas im Aussehen angepasst.

Stellt sich raus: Man verwendet nun endlich einen Adblocker. In diesem Fall uMatrix. Und uMatrix hat u.a. das Feature sog. HTTP-Referer für andere Seiten zu verbergen.
Normalerweise enthält der Referrer die Adresse der Webseite über die ich auf eine andere Webseite gekommen bin.

Suche ich z.B. auf Google nach einem Problem und klicke auf eine der Webseiten in den Ergebnissen, dann wird der Referrer an die aufrufende Webseite übermittelt. Somit kann man auswerten von wo ein Besucher auf die Webseite kam und wonach er gesucht hat. Durchaus relevante Informationen für viele Webseitenbetreiber. Aber natürlich unter Umständen ein Verlust an Privatsphäre für den Benutzer.

Daher ersetzt uMatrix den Referrer durch einen anderen Wert. Dies ist hier beschrieben: https://github.com/gorhill/uMatrix/wiki/Per-scope-switches#spoof-referer-header

Allerdings basiert die web.de/GMX Weiterleitung der Links auf dem HTTP-Referer. Da uMatrix diese Daten aber ersetzt, weiß die Weiterleitung nicht wohin sie weiterleiten soll und man erhält den Fehler 403 (welcher vermutlich für HTTP-403 Forbidden steht).

Die Lösung des Problems

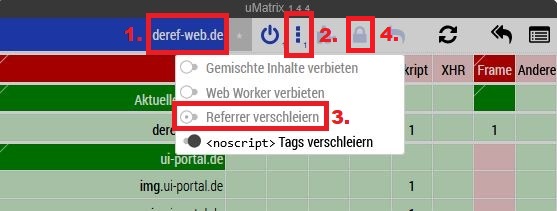
Die Option das der Referer ersetzt wird nennt sich "Referrer verschleiern" und findet sich im Menü von uMatrix. Dies ist über die 3 Punkte zu erreichen.

Konkret müssen wir bei web.de dies für die Domains navigator.web.de & deref-web.de deaktivieren.
Bei GMX analog für die Domain der Weboberfläche und von deref-gmx.de.

Zuerst öffnen wir die Übersicht von uMatrix indem wir auf das Symbol von uMatrix klicken (üblicherweise rechts neben der Adresszeile).

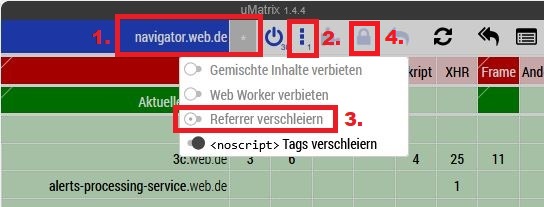
Schritt 1: Wir ändern den Bereich auf navigator.web.de so das die Änderungen exakt nur für diese Domain gilt. Als Standard ist hier web.de ausgewählt, das wollen wir aber nicht. Also sicherstellen dass das komplette Feld blau hervorgehoben ist.

Schritt 2: Wir klicken auf das 3 Punkte Menü

Schritt 3: Wir deaktivieren die "Referrer verschleiern" Option, so das diese, wie im Bild, ausgegraut ist.

Schritt 4: Anschließend auf das nun blau hervorgehobene Schloß-Symbol klicken um die Änderungen zu speichern.

Nun müssen wir dies noch einmal exakt genau so für die Domain deref-web.de bzw. deref-gmx.de durchführen. Hierzu genügt es einfach auf einen Link in einer Mail zu klicken, so das sich die Seite mit der Fehlermeldung öffnet.

Schritt 1: Wir belassen den Bereich auf deref-web.de bzw. deref-gmx.de. Da wir hier keine Subdomain haben, ist dies bereits korrekt ausgewählt.

Schritt 2: Wir klicken auf das 3 Punkte Menü

Schritt 3: Wir deaktivieren die "Referrer verschleiern" Option, so das diese, wie im Bild, ausgegraut ist.

Schritt 4: Anschließend auf das nun blau hervorgehobene Schloß-Symbol klicken um die Änderungen zu speichern.

Nun am besten zur Sicherheit einmal den Browser komplett beenden, mindestens aber den Tab mit der web.de/GMX Weboberfläche neu laden.

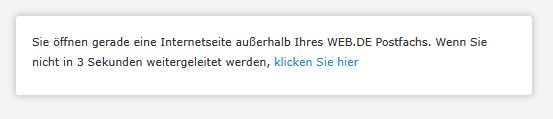
Klickt man dann auf einen Link sollte der gewohnte Weiterleitungshinweis erscheinen und man nach wenigen Sekunden auf der eigentlichen Seite sein.

Comments

Puppet is dead. Long live OpenVox!

Photo by cottonbro studio: https://www.pexels.com/photo/people-toasting-wine-glasses-3171837/

This is an update to my previous blogpost Puppet goes enshittyfication (Updated).

I the meantime the fork has happened. It's called OpenVox (https://github.com/openvoxproject) in reference to VoxPupuli - the name of community of module maintainer, authors and various other contributors around Puppet. But as we all now know, the community is dead. At least for Perforce. Well... As long as they can't get any real money out of it anyways..

The most non-surprising part? As of now there are no officially maintained container images for Puppet anymore.

Martin Alfke's betadots GmbH took over the maintenance of the puppetserver and puppetdb container images. As Puppet by Perforce did abandon them years ago. Now with the fork happening and Puppet effectively being a closed-source software product - and depending on how it develops - little to absolutely no support from Perforce, it simply makes no sense for the betadots GmbH anymore to do the free work for Puppet by Perforce. And they did so effective immediately. Understandably.

Hence they will be maintaining the openvoxserver & openvoxdb container images.

They announced this in a post on their betadots dev.to blog, in german but translation should work well. Read it here: https://dev.to/betadots/das-neue-puppet-open-source-projekt-heisst-openvox-2330

A questionable decision...

This means that in 2025 there are no container images for Puppet with official vendor support.

And as much as I like how this shows the power of a strong open source community...

I can't find a phrase strongly worded enough to describe this utter strategic mismanagement, so just look at this picture instead:

Photo by Photo By: Kaboompics.com: https://www.pexels.com/photo/a-short-haired-woman-holding-a-pair-of-eyeglasses-4491435/

Comments